This guide explains how to evaluate Havi Nextgen, from realistic pricing considerations to supplier due diligence and practical requirements. Objectively, it outlines what “nextgen” solutions typically involve—workflow modernization, standardized support, and compatibility checks—so buyers can compare options responsibly and choose with confidence.
If you’re considering Havi Nextgen, the smartest starting point is not marketing claims—it’s a structured evaluation of total cost, supplier responsibility, and operational requirements. This guide is designed to help decision-makers compare options methodically, clarify what’s included in the package, and verify that the solution aligns with real deployment conditions.
Because the keywords provided include placeholder segments, this article focuses on the actionable themes that typically accompany evaluations of next-generation offerings: what buyers should ask, how to validate delivery scope, and how to reduce implementation risk. Where pricing and supplier details are involved, the emphasis is on how to interpret them consistently—item by item—rather than assuming a universal figure.
In many procurement processes, “price” is only one line in a bigger document. For Havi Nextgen-type purchases, the very important variables often include implementation services, ongoing support, performance expectations, and compatibility requirements. A credible supplier can usually provide a clear scope-of-work, installation plan, and support policy in writing.
From an industry expert’s perspective, buyers should treat the decision like an operational project rather than a one-time transaction. That means confirming what is covered, what will be delivered, and how issues are handled after go-live—especially if multiple stakeholders (IT, operations, procurement, and security) are involved.
This expanded evaluation approach also helps you avoid a common trap: vendors may demonstrate the product successfully in a controlled environment, but your organization must validate how it behaves under your constraints—your devices, your network, your roles, your audit requirements, your data patterns, and your daily operational cadence.
“Nextgen” solutions in business environments usually aim to reduce friction between people, processes, and technology. For Havi Nextgen, the core value proposition—based on common industry patterns—tends to revolve around:
However, these benefits only materialize when the implementation plan matches the buyer’s environment. That’s why the evaluation process should focus on requirements verification—network, devices, user roles, access controls, and operational constraints.
To ground the “fit” discussion, it helps to define what “Nextgen” means in measurable terms. For example, “standardized workflows” should map to reduced error rates, improved throughput, fewer manual steps, and clearer audit trails. “Integration readiness” should map to working interfaces with known reliability and documented testing. “Support and maintainability” should map to response targets, resolution definitions, update cadence, and fallback options. “Scalability” should map to performance under higher load, manageable configuration growth, and predictable costs.
When you request these measurements up front, you reduce the chance of landing in a scenario where the solution is technically correct but operationally painful. Operational pain often appears as delayed onboarding, misaligned responsibilities, unclear escalation, and poor change management—issues that don’t show up in a typical demo.
When people search for Havi Nextgen, they often want a straightforward “price.” In practice, procurement teams get the top outcomes when they convert price inquiries into a pricing breakdown.
At minimum, request an offer that specifies:
Expert recommendation: Compare offers only after normalizing the scope. Two vendors can quote different numbers while actually delivering similar totals once add-ons and responsibilities are aligned.
If a supplier provides a “starting price” without clarifying inclusions, treat it as a preliminary figure. Ask for a line-item estimate or a total cost of ownership (TCO) view over a defined evaluation horizon (for example, the first 12–36 months). TCO comparisons should use consistent assumptions.
To make TCO comparisons realistic, you need to identify not just what you pay, but what you’ll spend internally: internal time for stakeholders, testing effort, security reviews, training time, and transition management. Even if vendors don’t charge for these costs, they become real schedule risks and budget impacts.
Below are common pricing elements that buyer teams should ask about for next-generation implementations. Even if you believe the vendor will include them, ask anyway—because “included” is often conditional.
When these items are missing, “cheap” offers can become expensive because hidden scope creep appears during delivery.
It’s also critical to define the commercial mechanics around pricing. For example:
These questions reduce disputes later. Good suppliers document answers clearly and are comfortable aligning commercial terms with operational reality.
Supplier selection for Havi Nextgen-type deployments should emphasize accountability. An objective way to assess supplier quality is to examine how they document and manage delivery.
Strong supplier practices generally include:
From an industry standpoint, the biggest deployment failures typically occur when responsibility boundaries are unclear—especially around integrations, security review, or data migration (if applicable). Therefore, insist on a written implementation plan.
To make due diligence more concrete, evaluate supplier responses in three layers: process, evidence, and people.
Ask for documentation that shows how they run projects:
Suppliers with mature processes will answer with structured artifacts rather than vague assurances.
“Reference cases” and “it worked for others” aren’t enough. Ask for evidence that directly relates to your environment:
Evidence doesn’t have to be proprietary. Many suppliers can share redacted documentation, anonymized results, or summary reports.
Implementation quality is frequently determined by the team’s capabilities and availability. Ask for:
Even the best plan can fail if the team is understaffed or if the supplier relies on unverified subcontractors. Clear resourcing commitments reduce implementation risk.
To determine whether Havi Nextgen is the right choice, buyers should evaluate requirements in four categories: operational, technical, security/compliance, and commercial.
In practice, “fit” should be interpreted as the likelihood that your organization can successfully operate the system day-to-day with acceptable risk. Fit is not solely about features; it’s about feasibility under real constraints.
Operational fit is often where “next-generation” projects succeed or fail. A vendor can implement a system technically, but if the workflows change in ways that users can’t adopt quickly, adoption becomes slow and quality drops.
When evaluating operational fit, ask for role-based workflow mapping. For example:
Also ask about operational constraints. For instance, do users operate during specific shifts? Is there downtime tolerance? Are there offline or low-connectivity scenarios? If your organization has seasonal spikes or planned disruptions, ensure the supplier plan accounts for those patterns.
Training evaluation should also consider:
Process ownership evaluation should include who maintains configuration. Many projects fail when the buyer lacks internal ownership after go-live. Ensure the contract includes a handover process and runbooks so internal teams can maintain the solution.
Technical fit must be validated with specifics. “It integrates” is not enough. You need to know the interface type, data format, authentication mechanism, rate limits, and operational behavior when an external system fails.
When reviewing Havi Nextgen technical fit, request an integration matrix that includes:
Additionally, performance expectations should be articulated in terms of what “good” looks like in your environment. Ask how performance is measured and what metrics are available. For example:
Infrastructure constraints should not be treated as an afterthought. Confirm network bandwidth and latency expectations, any required firewall rules, certificate requirements, and device compatibility. If the solution needs client agents or browser compatibility, ensure those dependencies are clearly listed.
Also evaluate operational dependencies:
Good technical fit reduces the risk of “it works in staging but breaks in production.” Ask for staging-to-production assumptions and how they validate equivalence.
Security and compliance fit is not just about meeting a checklist. It’s about ensuring the solution can be operated in a secure and auditable manner over time.
When evaluating security fit, ask for documentation and details related to:
Compliance requirements vary by organization. If you’re in a regulated industry, verify whether the supplier can provide artifacts for audits (for example, SOC reports, penetration testing summaries, or formal security documentation). Even if the buyer doesn’t need a full audit pack immediately, you want to know whether it exists.
Also evaluate incident readiness. Ask:
A major “fit” test is whether security review can be completed efficiently. If security artifacts are missing or incomplete, implementation might stall during review cycles.
Commercial fit is the operational contract translated into governance. It should align with how you plan to run the solution.
Key commercial questions include:
Acceptance criteria should be precise and testable. Avoid vague acceptance phrases like “the system performs as expected.” Instead, define test cases mapped to workflows, integrations, and security requirements. Make acceptance a joint process: supplier provides evidence, buyer verifies, and both agree on results.
Change management should specify how scope changes are handled. In next-generation deployments, scope changes are common because integration realities can emerge only once testing begins. A mature change-control process prevents friction by establishing a predictable workflow.
While the exact product scope behind Havi Nextgen can vary by market and deployment model, the broader industry background is consistent: buyers increasingly evaluate “next-generation” offerings using measurable outcomes and governance controls, not only feature lists. This trend is supported by widely used frameworks in technology procurement and risk management.
For instance, many organizations align purchasing decisions with:
Reliable references to consider during evaluation: NIST publications on risk management and cybersecurity governance, as well as IT service management practices described by ITIL guidance. These resources can help buyers structure questions and confirm that the supplier’s approach aligns with recognized risk and service-management principles.
Even if your procurement team doesn’t use these frameworks directly, their concepts translate into real-world decision questions. For example, NIST-style thinking encourages you to ask about risk likelihood and impact, not merely features. ITIL-style thinking encourages you to ask about incident categories, service desk processes, escalation, and service lifecycle management.
When applied to Havi Nextgen, these concepts result in concrete buyer actions: define acceptance criteria, ensure monitoring and auditability, formalize escalation and incident handling, and confirm update policies.
The following table supplements the main narrative with a structured comparison approach. It is intentionally designed to support buyer-side decision-making rather than promote any single offer.
| Evaluation area | What to look for when reviewing Havi Nextgen | Supplier conditions / requirements to request |
|---|---|---|
| Included scope | Confirm exactly what “Havi Nextgen” includes (core offering, onboarding, configuration, testing support) | Line-item scope-of-work; written inclusions/exclusions; acceptance criteria |
| Pricing structure | Validate whether the quote is product-only or also includes implementation and support | Itemized pricing; clear term length; renewal and upgrade policy |
| Implementation timeline | Check whether milestones are realistic for your environment and stakeholders | Project plan; milestone dates; responsibilities for buyer-prepared assets |
| Compatibility and integration | Assess whether existing systems can integrate without high rework | Integration matrix; interface details; testing plan and sign-off process |
| Support model | Evaluate support coverage after go-live (hours, escalation, response targets) | Support policy in writing; incident categories; escalation procedure |
| Security and compliance | Confirm access controls, logging, and data handling fit internal requirements | Security documentation; audit/logging capabilities; data retention terms |
| Change management | Ensure scope changes are handled transparently | Change-control process; how pricing for changes is determined |
| Operational handover | Check whether the buyer receives documentation and transition support for ongoing operations | Runbooks; admin guides; training for operations; handover schedule and responsibilities |
| Monitoring and reporting | Confirm what monitoring exists and what reporting is available for administrators | Monitoring plan; alert thresholds; dashboards; log export capabilities |
| Update and upgrade path | Understand how updates are handled and whether they require downtime | Update cadence; maintenance window expectations; backward compatibility statements |
Use this sequence to keep your evaluation objective and auditable.
To further increase your confidence, add two additional steps that often improve outcomes: (a) create a structured scorecard with weights aligned to your priorities, and (b) perform a “risk-to-cost” estimation for each offer so you understand which option reduces or increases operational risk.
Procurement teams often use scorecards but sometimes weight criteria incorrectly (for example, giving too much weight to features and too little to support and integration feasibility). For Havi Nextgen, a practical scoring model might include:
Scorecards are most effective when they define scoring rules. For each criterion, specify what “excellent,” “acceptable,” and “needs clarification” look like, and require evidence. This prevents subjective bias and helps align decision-makers.
Evidence-based scoring also strengthens internal approval by showing why a particular supplier was selected—beyond personal preference or a sales narrative.
Next-generation projects can fail for predictable reasons. Identify likely failure points early and ask targeted questions to prevent them. Common risk categories include:
When evaluating Havi Nextgen, ask suppliers to explicitly list assumptions. For example, “We assume the buyer will provide X access credentials,” “We assume the buyer will supply Y test data,” or “We assume integration endpoints will be available by date Z.” These assumptions create a shared understanding—and they help you plan your internal work.
Then, evaluate whether those assumptions are feasible for your organization. If the supplier assumes access or data preparation that your team cannot provide on time, the timeline risk is yours too.
To make evaluations efficient, use a question set that forces clarity. Below is a practical list of supplier questions you can adapt for Havi Nextgen. Even if you don’t ask all of them, ensure you ask enough to eliminate ambiguity.
When vendors can’t answer these directly, it often indicates they can’t commit to a clear delivery path. That doesn’t always mean the vendor is poor, but it should trigger deeper clarification before you sign.
A structured evaluation isn’t complete unless you validate scope item-by-item. For Havi Nextgen, scope ambiguity often appears in the difference between:
To reduce scope disputes, request an inclusion/exclusion list. For each major category, confirm:
Acceptance criteria should be written in measurable terms. For example, instead of “integration works,” define “integration will successfully transmit entity X from system A to system B with defined data mapping and error handling for scenario Y.”
A pilot is only valuable if it tests what you actually need. Many organizations run pilots that confirm the vendor’s happy path rather than your real complexity. Make the pilot meaningful by choosing scenarios aligned to:
To structure a pilot, define:
If the pilot fails, the reasons will be instructive. If the pilot succeeds but doesn’t cover critical requirements (security logging, integration failure handling, or admin workflows), you still may face issues during full rollout.
TCO is only as good as your assumptions. To compare Havi Nextgen offers fairly, define an evaluation horizon (12, 24, or 36 months) and include:
A practical TCO spreadsheet might contain columns for each vendor and rows for each cost element. Then normalize assumptions: same horizon, same scope, same training requirements, same number of integration endpoints, same required support tier.
Also consider whether the solution’s update mechanism influences cost. For example, if updates require your team to perform manual migrations, that becomes an ongoing internal cost.
Finally, do not overlook licensing assumptions. Verify whether licensing is based on users, devices, throughput, modules, or transactions. If the usage model is likely to grow, ask for the cost of growth. Many organizations regret selecting a license model that becomes expensive quickly.
Compatibility is the intersection of technical fit and operational fit. Integration issues can lead to partial failures, inconsistent data, and unpredictable user experience.
When validating integration, focus on “operational behavior,” not just connectivity. Ask for:
Also validate the administrative workflow around integrations. For example, who updates integration credentials? How are changes logged? How are integration outages communicated to internal teams?
Many organizations treat integration like a one-time engineering task, but it becomes an ongoing operational responsibility. A good supplier will include monitoring, runbooks, and support processes for integration health.
Security evaluation should not end at “it supports RBAC.” You need to confirm whether audit evidence exists and can be used internally.
Ask for specifics about audit trails:
Also clarify data lifecycle. For example, if data includes sensitive information, you need to know:
Operational security includes access governance. Ask how you can manage roles over time as staff changes. If you rely on manual role updates without automation or governance support, you may create security drift.
Security fit is often improved when the supplier offers clear documentation and supports your audit process. A supplier who provides security artifacts early reduces implementation delays.
Acceptance criteria are where you convert requirements into measurable outcomes. If they are vague, disputes are likely. If they are precise, delivery becomes more controllable.
Define acceptance criteria at three levels:
Use test cases where possible. For example:
Additionally, define the acceptance procedure. Who executes the tests? Who provides evidence? What qualifies as a defect? How are minor issues handled (severity levels)?
A mature supplier will collaborate on acceptance criteria and will be willing to align them with your internal standards.
Implementation timeline evaluation should be grounded in dependencies and stakeholder availability. A timeline with optimistic milestones often fails because critical prerequisites aren’t met.
When evaluating the Havi Nextgen project plan, examine:
Dependencies are critical. For example, integration testing may require external systems to provide test endpoints. Security review may require internal approvals and timely documentation. Data migration may require data extracts and mapping.
Ask each supplier to list their dependencies and the buyer’s responsibilities. Then validate your internal readiness.
Many organizations treat handover as a minor step. In reality, handover is one of the most important components of “fit.” If your operations teams can’t manage the system after go-live, the solution may degrade or remain underutilized.
Request handover deliverables such as:
Handover should also include training or workshops with the teams who will maintain the system. If supplier training is only for end-users, your operations team may still be unprepared.
Ask whether the supplier provides a formal knowledge transfer session and whether the buyer can schedule follow-ups during early operational weeks.
Support evaluation must go beyond hours and response targets. You need to understand the supplier’s support philosophy and mechanics.
Ask for:
Also clarify your escalation path. For example, if an incident is critical and blocked, what is the next escalation step? Is there an engineering escalation channel? What is the expected time to involve technical experts?
Support fit is often demonstrated by the supplier’s ability to produce clear incident categories and a mature escalation procedure.
Next-generation solutions are typically updated regularly. Update and upgrade policies affect your operations and security posture.
Ask suppliers about:
Also ask whether upgrades can be staggered or scheduled to avoid conflicts with peak operational periods. Without this, your timeline can be disrupted by vendor maintenance events.
From an evaluation standpoint, update policy also influences TCO. If frequent updates require extensive internal testing each time, the internal cost grows.
If you’re comparing more than one supplier for Havi Nextgen, use a consistent comparison template. Many organizations compare proposals informally and accidentally create bias. A structured approach improves fairness and decision quality.
Consider implementing a “proposal normalization” step:
Normalization also helps you detect when one vendor is shifting responsibilities. For instance, one vendor might appear cheaper because it excludes integration testing or security documentation. When normalized, the “cheaper” vendor might have higher total costs or higher operational risk.
Finally, conduct a structured review meeting with cross-functional stakeholders. IT and security often focus on technical feasibility and audit evidence, while operations focus on usability and support. Procurement focuses on commercial terms and risk allocation. A unified review reduces surprises later.
Pricing often varies by what is included. Ask for an itemized breakdown covering product/licensing, implementation or onboarding, training, support duration, maintenance or updates, and any required professional services. A complete quote should specify inclusions and exclusions clearly.
Also ask whether costs differ based on the environment (staging vs production) and whether multiple rollout phases require separate implementation charges.
Normalize the scope. Compare quotes only after aligning deliverables, support coverage, implementation milestones, and integration responsibilities. If one offer includes onboarding and another does not, compare total cost and effort on the same basis—not just the headline number.
For fairness, ensure that acceptance criteria and testing responsibilities are comparable. A vendor offering a lower price but requiring the buyer to perform major integration testing can increase your internal cost.
Request a scope-of-work, project plan with milestones, acceptance criteria, support policy, integration or compatibility statements, and security documentation related to access control and logging. Written documentation makes accountability measurable.
If applicable, ask for sample tickets, sample escalation examples, and templates for incident reporting. These artifacts help you gauge operational maturity.
Not automatically. “Nextgen” value is realized when the solution fits operational workflows, integrates with existing systems, and is supported effectively after rollout. Evaluate requirements fit and measurable outcomes rather than assuming newer equals better.
Sometimes older setups are sufficient if they meet security and operational needs. A “nextgen” solution becomes justified when it reduces risk, improves performance, or provides better governance and support maturity.
Typically, rollout depends on successful configuration, integration testing, user readiness, and security review. Suppliers should specify prerequisites and the buyer’s responsibilities. If prerequisites aren’t defined, implementation risk increases.
Also confirm operational readiness items like training completion, admin access assignment, monitoring dashboards availability, and support escalation contacts.
Ask how change management works: which milestones can move, how revised schedules are agreed, and how additional work is priced. A mature supplier will define a formal process for scope and timeline adjustments.
Additionally, confirm which dates are firm and which are based on assumptions. If the schedule depends on external system availability, ensure it’s realistic.
Many suppliers can support a proof step for high-risk components or workflows. Confirm what success criteria will be used, what costs apply, and how the results influence the full rollout scope.
Ask whether pilot learnings are formally translated into a revised implementation plan, rather than being treated as informal feedback.
Request details on access control, auditing/logging, data retention or lifecycle policies, and how incidents are handled. Align these with your internal security requirements and recognized risk management practices.
Where possible, validate that security artifacts are provided early enough to complete your review process before implementation milestones.
Choosing Havi Nextgen comes down to a disciplined evaluation: understand pricing as a structured set of deliverables, evaluate suppliers by their documented responsibilities and support maturity, and confirm that the solution fits your operational and technical requirements. When you compare offers using a normalized scope and objective acceptance criteria, you reduce uncertainty and increase the likelihood of a smooth, reliable rollout.
If you’d like, share the deployment context (industry, number of users, and which systems need integration). I can help you turn your priorities into a tailored requirement checklist and a supplier question set for Havi Nextgen.
Striking the Perfect Balance: Navigating Premiums and Out-of-Pocket Expenses in Senior Insurance Plans
Explore the Tranquil Bliss of Idyllic Rural Retreats
How to Make Lasting Memories at Disneyland Attractions
Affordable Phones and Plans for Seniors
Affordable Full Mouth Dental Implants Near You
Unlock the Top Kept Secrets to Finding Your Ideal Dentist for Flawless Dental Implant Results!
Discovering Springdale Estates
Unveiling RS Sul Telecom Services
The Guide to Car Trading
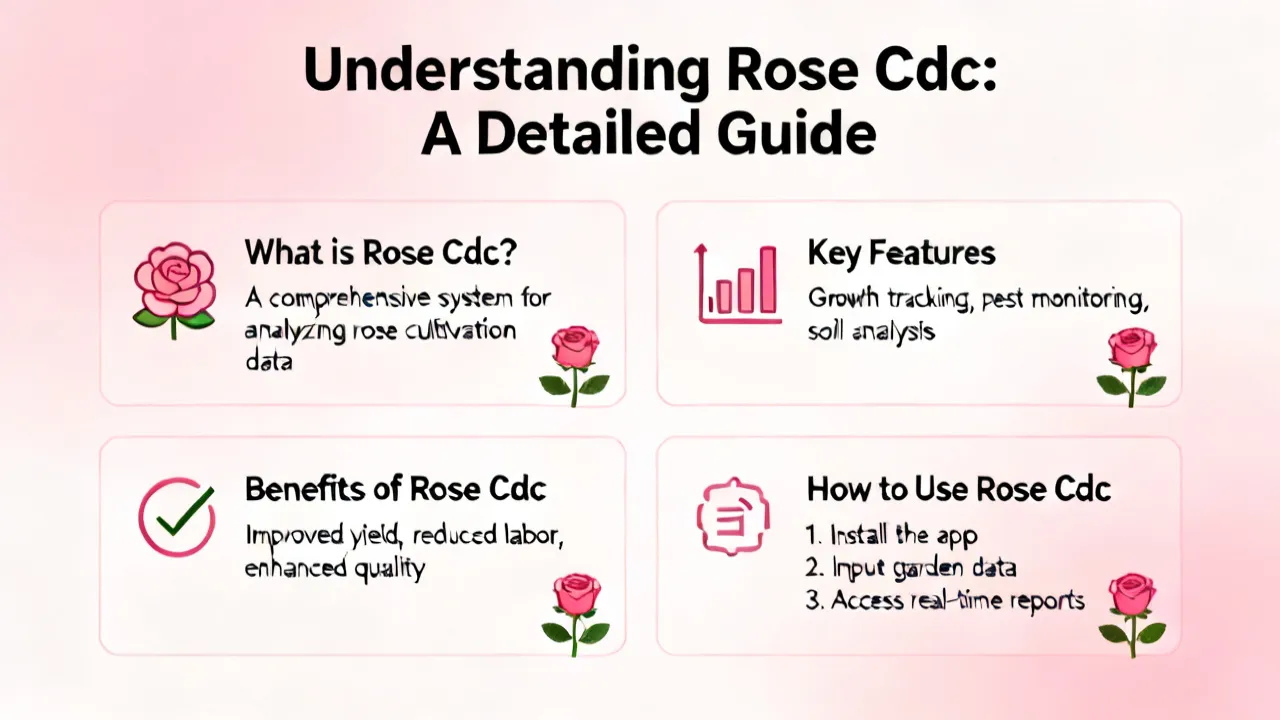
Understanding Rose Cdc: A Comprehensive Guide
This article provides an in-depth exploration of Rose Cdc, a term rapidly gaining attention in specific industries. Our discussion delves into the significance and application of Rose Cdc, its potential impact on various sectors, and expert insights into its future developments. This comprehensive analysis is designed to inform readers about the multifaceted aspects of Rose Cdc, its current applications, and potential advancements.
Understanding Compliance and AML Strategies
This article delves into the intricate realm of Compliance and Anti-Money Laundering (AML) strategies, highlighting their significance in the corporate world. Compliance AML refers to the organizational adherence to legal standards and regulations to deter financial crimes, ensuring transparent and ethical financial practices. This comprehensive guide examines these strategies' complexities and their pivotal role in safeguarding economic integrity.
Mastering Inbound B2B Strategies
The foundation of successful B2B strategies often lies in the effective implementation of inbound marketing techniques. In today's globally connected business environment, inbound B2B strategies have become critical for companies seeking to engage target audiences, optimize lead generation, and establish long-lasting partnerships. Understanding these strategies is essential for companies aiming to thrive in competitive markets.
Exploring B2B MBA Opportunities
Dive into the dynamic world of B2B MBA programs, designed for professionals seeking to enhance their strategic and management skills in a business-to-business context. This comprehensive guide discusses the significance of B2B MBAs in today's market, highlighting how these programs equip leaders with the expertise to navigate complex B2B relationships and drive business success.
Understanding Whitewater Regenerative Blowers
Whitewater Regenerative Blowers are essential in various industrial applications for their efficiency in moving air and gases. These blowers are known for their durability and ability to operate continuously, making them a preferred choice for industries ranging from wastewater treatment to aquaculture. This article explores their features, benefits, and applications, offering readers a comprehensive understanding of their importance in modern industry.
Mastering Employee Retention Strategies
Employee retention has become a critical aspect of organizational success, particularly in the dynamic landscape of 2020. As businesses strive to maintain a stable and productive workforce, understanding effective retention strategies is essential. This article delves into key methods for enhancing employee satisfaction and retention, offering a comprehensive guide for HR professionals and business leaders alike.